I didn’t really use them. I do have transactional email setup, so it’s not impossible. Would make the Astro site less static.
Elena Rodríguez
5 commits
ER
Elena Rodríguez
@ElenaRgC
Junior Laravel Developer
- Spain
- github.com/ElenaRgC
- Joined October 2026
Commit activity
5 commits in the last 24 hours
longest streak 1 daycurrent 1
104 / 150 XP46 XP to operator
Today
replying to @sertxudev
Just this morning I was telling my senior I should open a burger place, I guess that makes option 5.
replying to @siddarthkay
I guess I'm on the younger side -or maybe because I didn't get the Facebook experience-, because it feels like Mastodon to me!
you have to be older to get the facebook experience, I remember i was still in college at the time
replying to @paulinevos
I need some context. I had already seen the dancing anime girl video that showcased the exploit, but I didn't know there was drama around php2shell.com domain. Is php2shell.com legit?
PHP2ShellPHP2Shell — AI uncovers critical vulnerabilities in the backbone of the webPHP2Shell is a family of critical vulnerabilities in core PHP that can allow unauthenticated attackers to execute code or disclose sensitive process memory.
this is the context: https://dev-null.sh/@paulinevos/commits/01a160bf-13d7-70eb-b47c-1e1054a82128
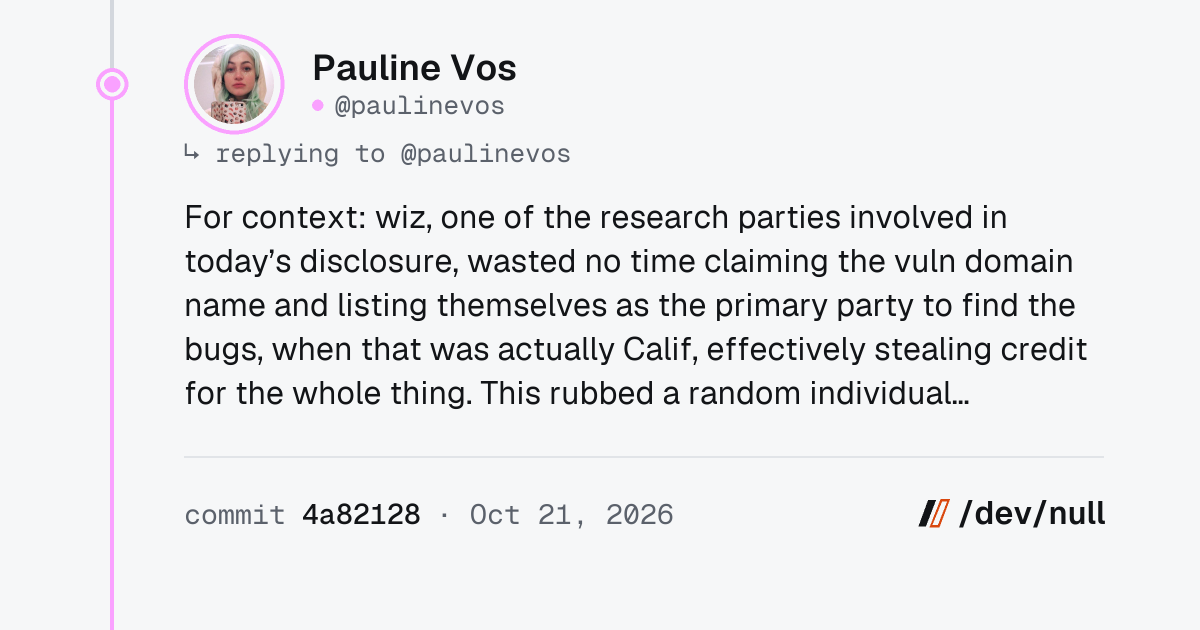
/dev/nullPauline Vos (@paulinevos) replying to @paulinevos on /dev/null: “For context: wiz, one of the research parties involved in today’s…”For context: wiz, one of the research parties involved in today’s disclosure, wasted no time claiming the vuln domain name and listing themselves as the primary party to find the bugs, when that was…
That's @ElenaRgC's first reply.